Cyberattacks that have marked the history of cybercrime
For years, it is easy to see that cyberattacks have improved.
The techniques used as well as the means developed are of a completely different level compared to a decade ago now. It is 10 years ago, for an individual to be the victim of a cyberattack was more a hypothesis than a real possibility.
Today, this is a fact and happens every day. For good reason, hackers know very well why they work this way. The status of the person, one should know what is a potential target and of choice above all. Especially with phishing and ransomware. Beyond all this we must mention the fact that cyberattacks are too sophisticated and numerous. "The volume of cyberattacks is increasing because our society is more digital and interconnected than before. Ten years ago, there were far fewer interconnections between computers, so it was less visible, the impact was more local. Today, it only takes a small element of fragility for the entire chain to be affected and a hospital to be completely shut down," explained Laura Peytavin, a consultant cybersecurity systems engineer at cybersecurity solutions publisher Proofpoint.
This article will also interest you: Cyberattacks: a response against the Microsoft attack would be underway
So here are some cyberattacks for you that by their scope and sophistication have marked the news in cybersecurity
1) Stuxnet, the forerunner of cyberwarfare
Stuxnet is virus that was updated in 2010. It was used to bring a text to Iran's nuclear program. It was introduced into targeted computer systems through the use of computer worms that presents itself as "malware that uses a vulnerability to break into a computer to try to hack all nearby devices using the same vulnerabilities," says Corinne Henin, an independent cybersecurity expert.
Stuxnet was designed by the American and Israeli services. This malware was then able to carry out nearly 30,000 Iranian computers, allowing the Allies here to take control of some of the infrastructure necessary for the operation of the uranium registration plant. This has caused several malfunctions of the tools even if to slow down the process or even explosions.
"This is the biggest interstate cyberattack that can be proven to be interstate," notes Corinne Henin. "Here, all the evidence has shown that the NSA is behind the hacking, whereas in other large-scale cyberattacks, it is much more complicated to incriminate one state or another," she adds.
2- Cyberbunker
The BBC declared in 2013 "the most significant cyberattack in history." A computer incident that slowed internet access on an ad hoc basis. This is because of a conflict between two IT companies, Cyberbunker and Spamhaus.
It should be noted that Spamhaus and a non-profit organization that aims to help email providers by helping them filter out unwanted content and spam. Cyberbunker, on the other hand, is seen as a host who takes responsibility for hosting any type of content except of course "except child pornography and everything related to terrorism." However, the latter is suspected of often hosting spam services, so it has been placed on the blacklist of the first. This resulted in computer revenge. Spamhaus has seen its servers affected by a denial-of-service attack. The result of the attack was the total slowdown of the web
3- WannaCry, the ransomware
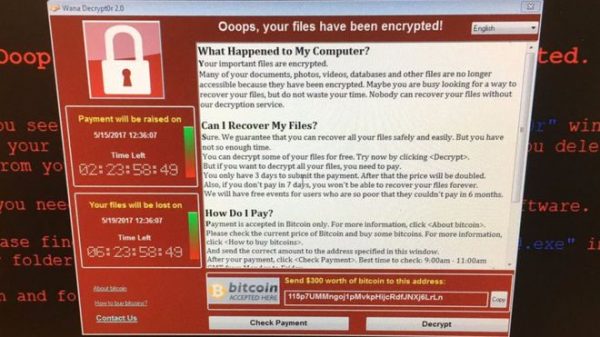
Today, it is arguably the most famous cyberattack. This hacking took place, at least officially started in 2017 precisely during the month of May. More than 300,000 computers worldwide, running on Microsoft's operating system, that is, Windows, have been infected. The virus originally spread, which was considered unheard of at the time. "A group of hackers then claimed to have hacked the NSA by revealing all its tools of the time. And among those tools was a Windows flaw — affecting up to Windows 10 — that was used a month later to create WannaCry," says Corinne Henin.
It should be noted that many Internet users and organizations were literally forced to pay the ransom in order to be able to recover their data. The damage caused by this cyberattack was estimated at US$4 billion. France was the fourth most affected country by this malware spread with nearly 20,000 computers infected. "Before, people didn't necessarily realize the problem. With WannaCry, they lost their data and access to their infrastructure… stresses the specialist.
Now access an unlimited number of passwords!